The flaw was a division by the modulus q whose operands relied on secret knowledge, in the routines that convert between polynomial coefficients and message bits. Miklós Ajtai confirmed in a 1996 paper on the Symposium on Theory of Computing that lattices escape this bind. He constructed a distribution of random situations with the property that an algorithm fixing a random occasion with non-negligible chance could be was an algorithm fixing each instance of a standard lattice drawback. Randomly generated lattice keys are due to this fact as hard as the toughest case, which is a assure no other major household provides.
NIST declined to standardise FrodoKEM as a outcome of ML-KEM, resting on the same Studying With Errors drawback, is extra efficient. The BSI’s guideline says that because FrodoKEM relies on unstructured lattices where ML-KEM just isn’t, it’s considered the extra conservative choice, which is the algebraic-structure worry described earlier on this web page turned into a national recommendation. Where the NSA’s TLS profile forbids something aside from pure ML-KEM-1024, the BSI recommends in opposition to pure post-quantum deployment entirely. Taken together they clarify why no one units parameters using the reduction, and why treating it as a safety proof is a category error rather than a small exaggeration.
Parameter Units And What They Price

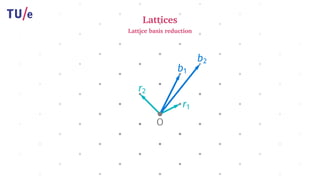
It generalises LLL by working on overlapping home windows of the idea rather than on pairs of vectors. A browser wants the first row, which is lattice-based cryptography, a firmware signer can reside with the third, and a satellite tv for pc that shall be in orbit for twenty years may moderately choose the second. The 2022 break described earlier eliminated SIKE and the key-exchange construction it was constructed on, and it did not remove the underlying problem. This is an operational hazard somewhat than a mathematical one, and operational hazards are those that actually happen.
In MDP, given a linear code CC over a finite subject, one must discover the non-zero codeword of minimum Hamming weight (codeword with the least number of 1’s). Notice that discovering the minimum distance of a binary linear code is NP-hard 23. The Minimum Distance Drawback (MDP) in code-based cryptography is very related to the Shortest Vector Downside (SVP) in lattice-based cryptography. Despite being distinct, linear codes and lattices are very similar at their core. In reality, one main similarity is that each linear codes and lattices are generated by bases.
- Nonetheless, quantum computers will have the ability to crack these systems rapidly utilizing Shor’s Algorithm, which is why research is currently being carried out into post-quantum cryptography to find cryptographic strategies that may stand up to assaults from quantum computer systems 1.
- Robert McEliece published a public-key cryptosystem based mostly on algebraic coding concept within the Deep House Community Progress Report for January and February 1978, and its central concept has by no means been broken.
- In a Learning with Errors (LWE) system we take some square array A.
- The submission reviews block sizes of 406, 626 and 878 for the three parameter units, and multiplying by 0.292 offers 118, 183 and 256 bits of classical core-SVP hardness, which is where the security-category claims come from.
The episode is a good image of how cryptanalysis of lattice-based cryptography truly works. A claimed improvement arrives, the numbers in everyone’s tables shift, a careful re-analysis finds the underlying heuristic unjustified, and the numbers shift back. Anybody reading a bit rely for lattice-based cryptography ought to understand that it’s a snapshot of an argument somewhat than a property of the algorithm. The published quantity is a floor that the authors themselves imagine is nicely under the truth, which is exactly what a floor should be.
Why Falcon’s Sampler Is So Hard To Write
Signatures in lattice-based cryptography work in one other way, as a outcome of there is no shared secret to agree on and no ciphertext to verify. ML-DSA, published as FIPS 204 and derived from CRYSTALS-Dilithium, follows a design template called Fiat-Shamir with Aborts, set out by Vadim Lyubashevsky at Asiacrypt 2009. Rather than drawing contemporary randomness from the machine, the sender hashes the message to obtain the randomness, in order that any given message always produces precisely one valid ciphertext. That single change turns a loose relation between plaintexts and ciphertexts into a function that can be checked.
Why Lattices Matter
It hands you a lattice and a quantity, and asks only whether or not the shortest vector is shorter than that number or greater than gamma times longer, with the promise that one of the two is true. Decision versions are easier to reason about in proofs, which is why they appear within the theorems despite the fact that no person deploys them. The NP-hardness results sound like the end of the argument, and they are not. They apply to the precise variations of the problems, or to approximation inside a small constant, and no cryptographic scheme depends on these.
ML-KEM is the standardised form of CRYSTALS-Kyber, published as FIPS 203 on thirteen August 2024, and the underlying scheme was described by Joppe Bos and colleagues at IEEE EuroS and P in 2018. Every Thing occurs in a hoop of polynomials of diploma lower than 256 with coefficients modulo the prime 3329, and the module rank is the single quantity that separates the three parameter sets. It is essentially the most widely deployed piece of lattice-based cryptography in existence.
There is a carve-out for hash-based signatures, the place hybridation is optional, which is in keeping with the argument, as a result of the hash assumption is the one no person doubts. In February 2022 Ward Beullens posted a paper whose title said everything. To avoid leaking the trapdoor, the lattice point have to be drawn from a discrete Gaussian distribution centred on the target, and doing that correctly requires floating-point arithmetic over a recursive tree structure. Implementing it in order that https://falcoware.com/FalcoManager.php the working time and reminiscence access pattern reveal nothing about the secret is way more durable than the integer arithmetic of ML-DSA, and getting it mistaken has produced sensible key-recovery attacks on earlier Gaussian-sampling signature schemes.